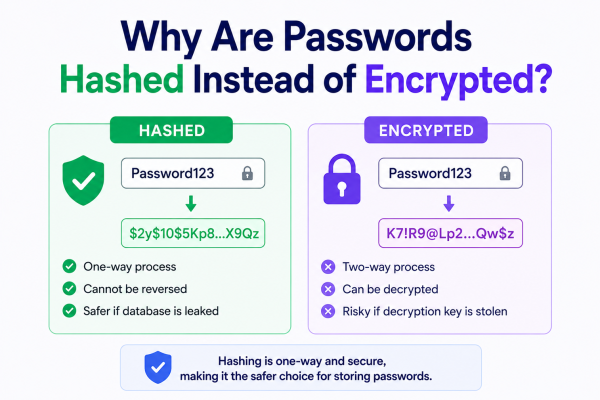
Why Are Passwords Hashed Instead of Encrypted?
A complete, beginner-to-production walkthrough of why every well-built login system stores password hashes instead of encrypted passwords: the 1962 MIT CTSS printer incident, Robert Morris Sr.’s 1970s Unix crypt-with-salt scheme, and the timeline through bcrypt (1999), PBKDF2 (2000), scrypt (2009), and Argon2id’s 2015 Password Hashing Competition win; the core motivation…